[1.21.*] ✅ EzAuth ✅ Login - 2FA - Email verification - Link
3.2.2Authentication, standalone 2FA and integration for Wordpress, Xenforo & more
EzAuth
Drop-in authentication for modern Paper and Bukkit servers with polished UX, standalone or integrated TOTP 2FA, and flexible storage.

Overview
EzAuth locks down your server's spawn with email-backed registrations, password logins, and time-limited sessions. Players are guided through the process with configurable messages, multi-language prompts (English, Nederlands, Español out of the box), visual effects, and reminders while administrators retain full control over storage backends, security policy, and optional SMTP settings. Toggle between pure login, opt-in 2FA, or a standalone two-factor flow that layers EzAuth's `/2fa` experience onto any existing authentication plugin. New: guide administrators through an in-game installation that immediately re-locks every active session when setup finishes, tap into the new session caching layer for instant post-login checks, then hook directly into Laravel, WordPress, or XenForo user tables so your website and server share a single account system.
[ NEW] Join the EzPlugins discord server for direct support
Try out our 2FA feature on mc.skyblockexp.com
Key Features
- Player-first onboarding – `/register` validates emails, enforces configurable password lengths, blocks duplicate emails or accounts, and saves asynchronously so players never stall the main thread.
- Guided ingame installation – `/ezauth install` walks staff through launch day setup, optionally bypasses the login guard until you're ready, and re-locks every active session the moment installation is marked complete.
- Localized messaging – Ship multiple language packs (English, Nederlands, Español by default), set your default language, and let players opt into their preferred message set on join.
- Hardened logins – `/login` honours staged cooldowns, respects bypass permissions, caches accounts for quicker checks, and runs password hashing off-thread before celebrating success with optional effects.
- Built-in TOTP two-factor – `/2fa` walks players through setup, confirmation, verification, status checks, and disabling while the TwoFactorService generates secure secrets and verifies codes. Flip `security.yml`'s `authentication-type` to `two_factor` to run EzAuth as a standalone 2FA module alongside plugins like AuthMe or via proxy networks.
- Session control – Movement, chat, and non-whitelisted commands are blocked until authentication completes, with five-second reminders and automatic session timeouts that can re-lock idle players.
- Session caching – Cache active authentications per-server and across proxies to trim database hits and keep trusted players online through quick restarts.
- Book-based prompts – Toggle `
authentication-input: book` to capture passwords and 2FA codes through an interactive written book, with automatic re-prompts if a player closes it early. - Celebratory polish – Toggle per-event particles and sounds or disable them globally from `security.yml`.
- Flexible storage – Choose YAML files, EzAuth-managed MySQL tables, or hook directly into Laravel, WordPress, and XenForo schemas via the new integration block while still storing accounts by UUID or username.
- Configurable hashing – Switch between BCrypt (custom rounds), SHA-256 with a pepper, or WordPress PHPass without touching code.
- Email-ready – `email.yml` exposes SMTP host, port, TLS/SSL, credentials, sender identity, and arbitrary mail properties so you're ready when outbound messaging lands.
- Email verification – Send verification codes to new registrations, block unverified logins, and let players confirm or resend their code with `/email` commands.
- Sensitive command filtering – Hide authentication attempts from console logs by listing sensitive commands in `security.yml` so staff chats stay clean while log filters update automatically on reloads.
- Admin oversight – `/ezauth players` opens a paginated in-game GUI with account email, creation time, and 2FA status so staff can disable two-factor or remove registrations without console commands.

Authentication Types
- Login – The classic EzAuth flow with `/register`, `/login`, and optional `/2fa` for layered security.
- Standalone 2FA – Keep your existing password solution but give players EzAuth's polished authenticator setup, code checks, and admin controls by setting `
authentication-type: two_factor`. Perfect for networks standardising on AuthMe, MultiAuth, or proxy-level SSO that still want in-game TOTP enforcement. - Optional – Let players secure their account when they're ready while you maintain traditional logins for everyone else.
Commands & Permissions
| Command | Usage | Permission | Default |
| /register | /register <email> <password> <password> | ezauth.register | Everyone |
| /login | /login <password> | ezauth.login | Everyone |
| /2fa, /twofactor | /2fa <setup|confirm|verify|disable|status> | ezauth.2fa | Everyone |
| /email <verify <code>|resend> | ezauth.email | Everyone | |
| - | - | ezauth.2fa.admin | OP |
| /ezauth | /ezauth reload | ezauth.reload | OP |
| /ezauth install | /ezauth install <status|complete|reset|config> | ezauth.install | OP |
| - | - | ezauth.bypass | OP |
Guided In-game Installation
Launch EzAuth for the first time and let the new installation workflow do the heavy lifting:
- Use `/ezauth install status` to confirm the guided flow is active and view whether the login guard is temporarily bypassed.
- Tweak installation options in-game with `/ezauth install config` to enable reminders, disable bypass mode, or re-open the GUI later.
- Once your storage, hashing, and security files look right, finish with `/ezauth install complete` to re-lock every connected player until they authenticate.
- Need to re-run onboarding for a new season? `/ezauth install reset` re-opens the flow without touching existing accounts.
Quick Configuration Presets
Pick the baseline that matches your deployment, copy the snippets into your generated configs, and tweak credentials or feature toggles as needed.
YAML Storage + Password Login
- Perfect for single-server setups that don't need a database. Accounts are saved to disk and BCrypt keeps passwords safe.
# Use the lightweight YAML storage backend.
storage-type: yml
account-identifier: uuid
yaml-file: registrations.yml
integration:
  mode: none
# Stick with secure BCrypt hashing.
algorithm: bcrypt
bcrypt:
rounds: 10# Default login flow with optional particles disabled for quieter servers.
authentication-type: login
particles-enabled: false
sounds-enabled: falseManaged MySQL + Login
- Stores players in EzAuth's MySQL schema while retaining the classic `/register` + `/login` experience.
storage-type: mysql
account-identifier: uuid
host: localhost
port: 3306
name: ezauth
username: ezauth
password: changeme
jdbc-parameters: useSSL=false&allowPublicKeyRetrieval=true&serverTimezone=UTC
integration:
  mode: none
algorithm: bcrypt
bcrypt:
rounds: 12authentication-type: login
session:
timeout-minutes: 15
particles-enabled: true
sounds-enabled: trueStandalone 2FA Module
- Pair EzAuth with another authentication plugin and only use it for `/2fa` management.
storage-type: mysql
account-identifier: uuid
host: localhost
port: 3306
name: ezauth
username: ezauth
password: changeme
jdbc-parameters: useSSL=false&allowPublicKeyRetrieval=true&serverTimezone=UTC
integration:
  mode: none
# Hashing is unused in standalone 2FA mode but keep defaults for compatibility.
algorithm: bcrypt
bcrypt:
rounds: 10authentication-type: two_factor
two-factor:
standalone-mode: true
enforce-on-join: true
session:
timeout-minutes: 10WordPress Integration + Shared Accounts
- Connect Minecraft logins to your existing WordPress site and sync optional two-factor status.
storage-type: mysql
account-identifier: username
host: localhost
port: 3306
name: wordpress
username: wp_user
password: supersecret
jdbc-parameters: useSSL=false&characterEncoding=UTF-8
integration:
  mode: wordpress
  wordpress:
    table-prefix: wp_
    users-table: wp_users
    user-meta-table: wp_usermeta
    username-column: user_login
    email-column: user_email
    password-column: user_pass
    uuid-meta-key: minecraft_uuid
    two-factor-secret-meta-key: ezauth_2fa_secret
    two-factor-confirmed-meta-key: ezauth_2fa_confirmed
algorithm: wordpressauthentication-type: login
two-factor:
optional: true
locale:
default-language: en_USDefault Configuration
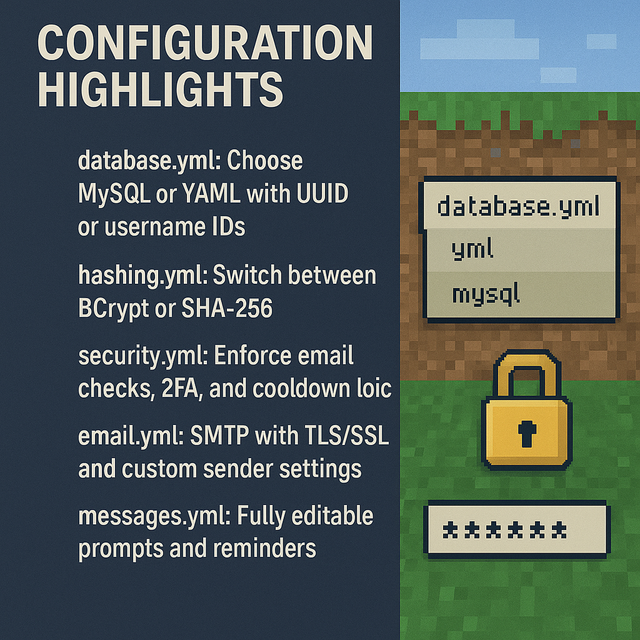
`database.yml` now includes an `integration` section so you can reuse Laravel, WordPress, or XenForo tables while keeping EzAuth's familiar commands. Update the table and column names to match your deployment or leave the mode on `none` to keep EzAuth's managed schema.
database.yml
# EzAuth Storage Configuration
# Choose how player registrations are stored. Supported values are `yml` and `mysql`.
storage-type: yml

# Controls how player accounts are looked up. Supported values are `uuid` and `username`.
account-identifier: uuid

# Configuration for the YAML storage backend.
yaml-file: registrations.yml

# MySQL connection details (only used when storage-type is `mysql`).
host: localhost
port: 3306
name: ezauth
username: root
password: password
# Additional JDBC parameters appended to the JDBC URL.
jdbc-parameters: useSSL=false&allowPublicKeyRetrieval=true&serverTimezone=UTC
pool:
  maximum-pool-size: 10
  minimum-idle: 2
  connection-timeout: 30000
  idle-timeout: 600000
  max-lifetime: 1800000
  data-source-properties:
    cachePrepStmts: "true"
    prepStmtCacheSize: "250"
    prepStmtCacheSqlLimit: "2048"

# Integration options are only used when storage-type is `mysql`. Configure EzAuth to reuse
# existing authentication tables from popular web frameworks or set the mode to `none` to
# manage accounts with EzAuth's own schema.
integration:
  # Supported values: none, laravel, wordpress, xenforo
  mode: none
  laravel:
    table: users
    uuid-column: uuid
    username-column: name
    email-column: email
    password-column: password
    two-factor-secret-column: two_factor_secret
    two-factor-confirmed-column: two_factor_confirmed
    created-at-column: created_at
    updated-at-column: updated_at
    remember-token-column: remember_token
  wordpress:
    table-prefix: wp_
    users-table: wp_users
    user-meta-table: wp_usermeta
    username-column: user_login
    email-column: user_email
    password-column: user_pass
    created-at-column: user_registered
    uuid-meta-key: minecraft_uuid
    two-factor-secret-meta-key: ezauth_two_factor_secret
    two-factor-confirmed-meta-key: ezauth_two_factor_confirmed
  xenforo:
    table-prefix: xf_
    user-table: xf_user
    user-auth-table: xf_user_authenticate
    user-field-value-table: xf_user_field_value
    user-profile-table: xf_user_profile
    username-column: username
    email-column: email
    created-at-column: register_date
    uuid-field-id: minecraft_uuid
    two-factor-secret-field-id: ezauth_two_factor_secret
    two-factor-confirmed-field-id: ezauth_two_factor_confirmed
WordPress setups need a few extra tweaks before going live:
- Switch `hashing.yml`'s `algorithm` to `WORDPRESS_PHPASS` so EzAuth produces hashes compatible with WordPress' PHPass implementation.
- Keep the UUID and two-factor meta keys (`minecraft_uuid`, `ezauth_two_factor_secret`, `ezauth_two_factor_confirmed` by default) or adjust them to match your existing data.
- Update the table prefix or table names if your WordPress instance uses a custom prefix.
XenForo deployments should create three custom text user fields in the XenForo control panel matching the configured
`uuid-field-id`, `two-factor-secret-field-id`, and `two-factor-confirmed-field-id`. EzAuth keeps the values in
`xf_user_field_value`, `xf_user_profile.custom_fields`, and `xf_user_authenticate` aligned whenever it updates an account.
Laravel schemas should expose UUID and two-factor columns alongside the framework defaults (`remember_token`, `created_at`, `updated_at`).
If you use Jetstream or Breeze, add the following migration so EzAuth can reuse your user table without data loss:
Laravel migration
Schema::table('users', function (Blueprint $table) {
    $table->uuid('uuid')->unique()->after('id');
    $table->text('two_factor_secret')->nullable()->after('password');
    $table->boolean('two_factor_confirmed')->default(false)->after('two_factor_secret');
});
EzAuth keeps the two-factor values intact when it updates an existing Laravel user and will fill in timestamps and the remember token for fresh rows.
hashing.yml
# EzAuth Hashing Configuration
# Configure the password hashing algorithm and its options.
# Supported algorithms: BCRYPT, SHA256, WORDPRESS_PHPASS
algorithm: BCRYPT
bcrypt:
  rounds: 10
sha256:
  pepper: ""
security.yml
# EzAuth Security Configuration
# Configure registration, login, and two-factor authentication behaviour.
require-email-validation: true
min-password-length: 8
session-timeout-seconds: 300
login-enabled: true
register-enabled: true
bypass-enabled: true
login:
  cooldown:
    enabled: true
    stages:
      - attempts: 3
        cooldown-seconds: 10
      - attempts: 5
        cooldown-seconds: 60
two-factor:
  enabled: false
  issuer: EzAuth
  required-for-login: false
  # Optional messages sent to players after they successfully secure their account with 2FA.
  # Supports either a single string or a list of lines. Set to an empty list ([]) to disable.
  secure-account-welcome-message:
    - "%prefix%&aTwo-factor authentication is now enabled for your account, %player%!"
allowed-commands-while-unauthenticated:
  - login
  - register
  - 2fa
  - twofactor
visual-effects:
  enabled: true
  login:
    enabled: true
    particle: VILLAGER_HAPPY
    particle-count: 30
    particle-offset-x: 0.0
    particle-offset-y: 1.0
    particle-offset-z: 0.0
    particle-spread-x: 0.25
    particle-spread-y: 0.35
    particle-spread-z: 0.25
    sound: ENTITY_PLAYER_LEVELUP
    sound-volume: 1.0
    sound-pitch: 1.2
  register:
    enabled: true
    particle: FIREWORKS_SPARK
    particle-count: 50
    particle-offset-x: 0.0
    particle-offset-y: 1.0
    particle-offset-z: 0.0
    particle-spread-x: 0.4
    particle-spread-y: 0.6
    particle-spread-z: 0.4
    sound: UI_TOAST_CHALLENGE_COMPLETE
    sound-volume: 1.0
    sound-pitch: 1.0
security.yml (2FA-only mode)
# EzAuth Security Configuration (2FA-only mode)
# Disable password registration/login while keeping Two-Factor Authentication available as an opt-in layer.
# Also removes the bypass permission so every player must authenticate with 2FA once enrolled.
require-email-validation: false
min-password-length: 8
session-timeout-seconds: 0
login-enabled: false
register-enabled: false
bypass-enabled: false
login:
  cooldown:
    enabled: false
    stages: []
two-factor:
  enabled: true
  issuer: EzAuth
  required-for-login: false
  secure-account-welcome-message:
    - "%prefix%&aTwo-factor authentication is now enabled for your account, %player%!"
allowed-commands-while-unauthenticated:
  - 2fa
  - twofactor
visual-effects:
  enabled: false
email.yml
# EzAuth Email Configuration
# Configure optional SMTP settings for outbound email integrations.
# Set enabled to true and provide the remaining settings to allow EzAuth to
# connect to your mail provider. Leave disabled to skip email setup entirely.
enabled: false
host: localhost
port: 587
username: ''
password: ''
use-tls: true
use-ssl: false
from-address: [email protected]
from-name: EzAuth
# Additional mail session properties may be configured below. For example:
# properties:
#   mail.debug: 'true'
properties: {}Similar projects
Plugin →Let Me Despawn
Improves performance by tweaking mob despawn rules. Say bye to pesky unintentional persistent mobs.
25MSueta
JourneyMap
Real-time map used for mapping in-game or your browser as you explore.
14.7MSueta
Emotecraft
Create your own emotes in Minecraft.
7.5MSueta
Simple Tpa
A simple tpa plugin which sends requests
5.4MSueta
Common Network
Forge and Fabric Unified Networking Solution
3.9MSueta
Set Home
A lightweight plugin for players to set their homes.
3.8MSueta